Risk management
Cyber Risk Management Without Enterprise GRC Complexity
Get cyber risk out of spreadsheets without an enterprise GRC programme: what Swedish rules require, and what to have in place.
Resources
Practical guidance on NIS2, maturity assessments, and building resilient security programmes across European organisations.
Get cyber risk out of spreadsheets without an enterprise GRC programme: what Swedish rules require, and what to have in place.
A long list of security controls looks strong on paper but says little about resilience. Learn how to focus your security budget on the risks that matter most, and what proportionate security means under NIS2.
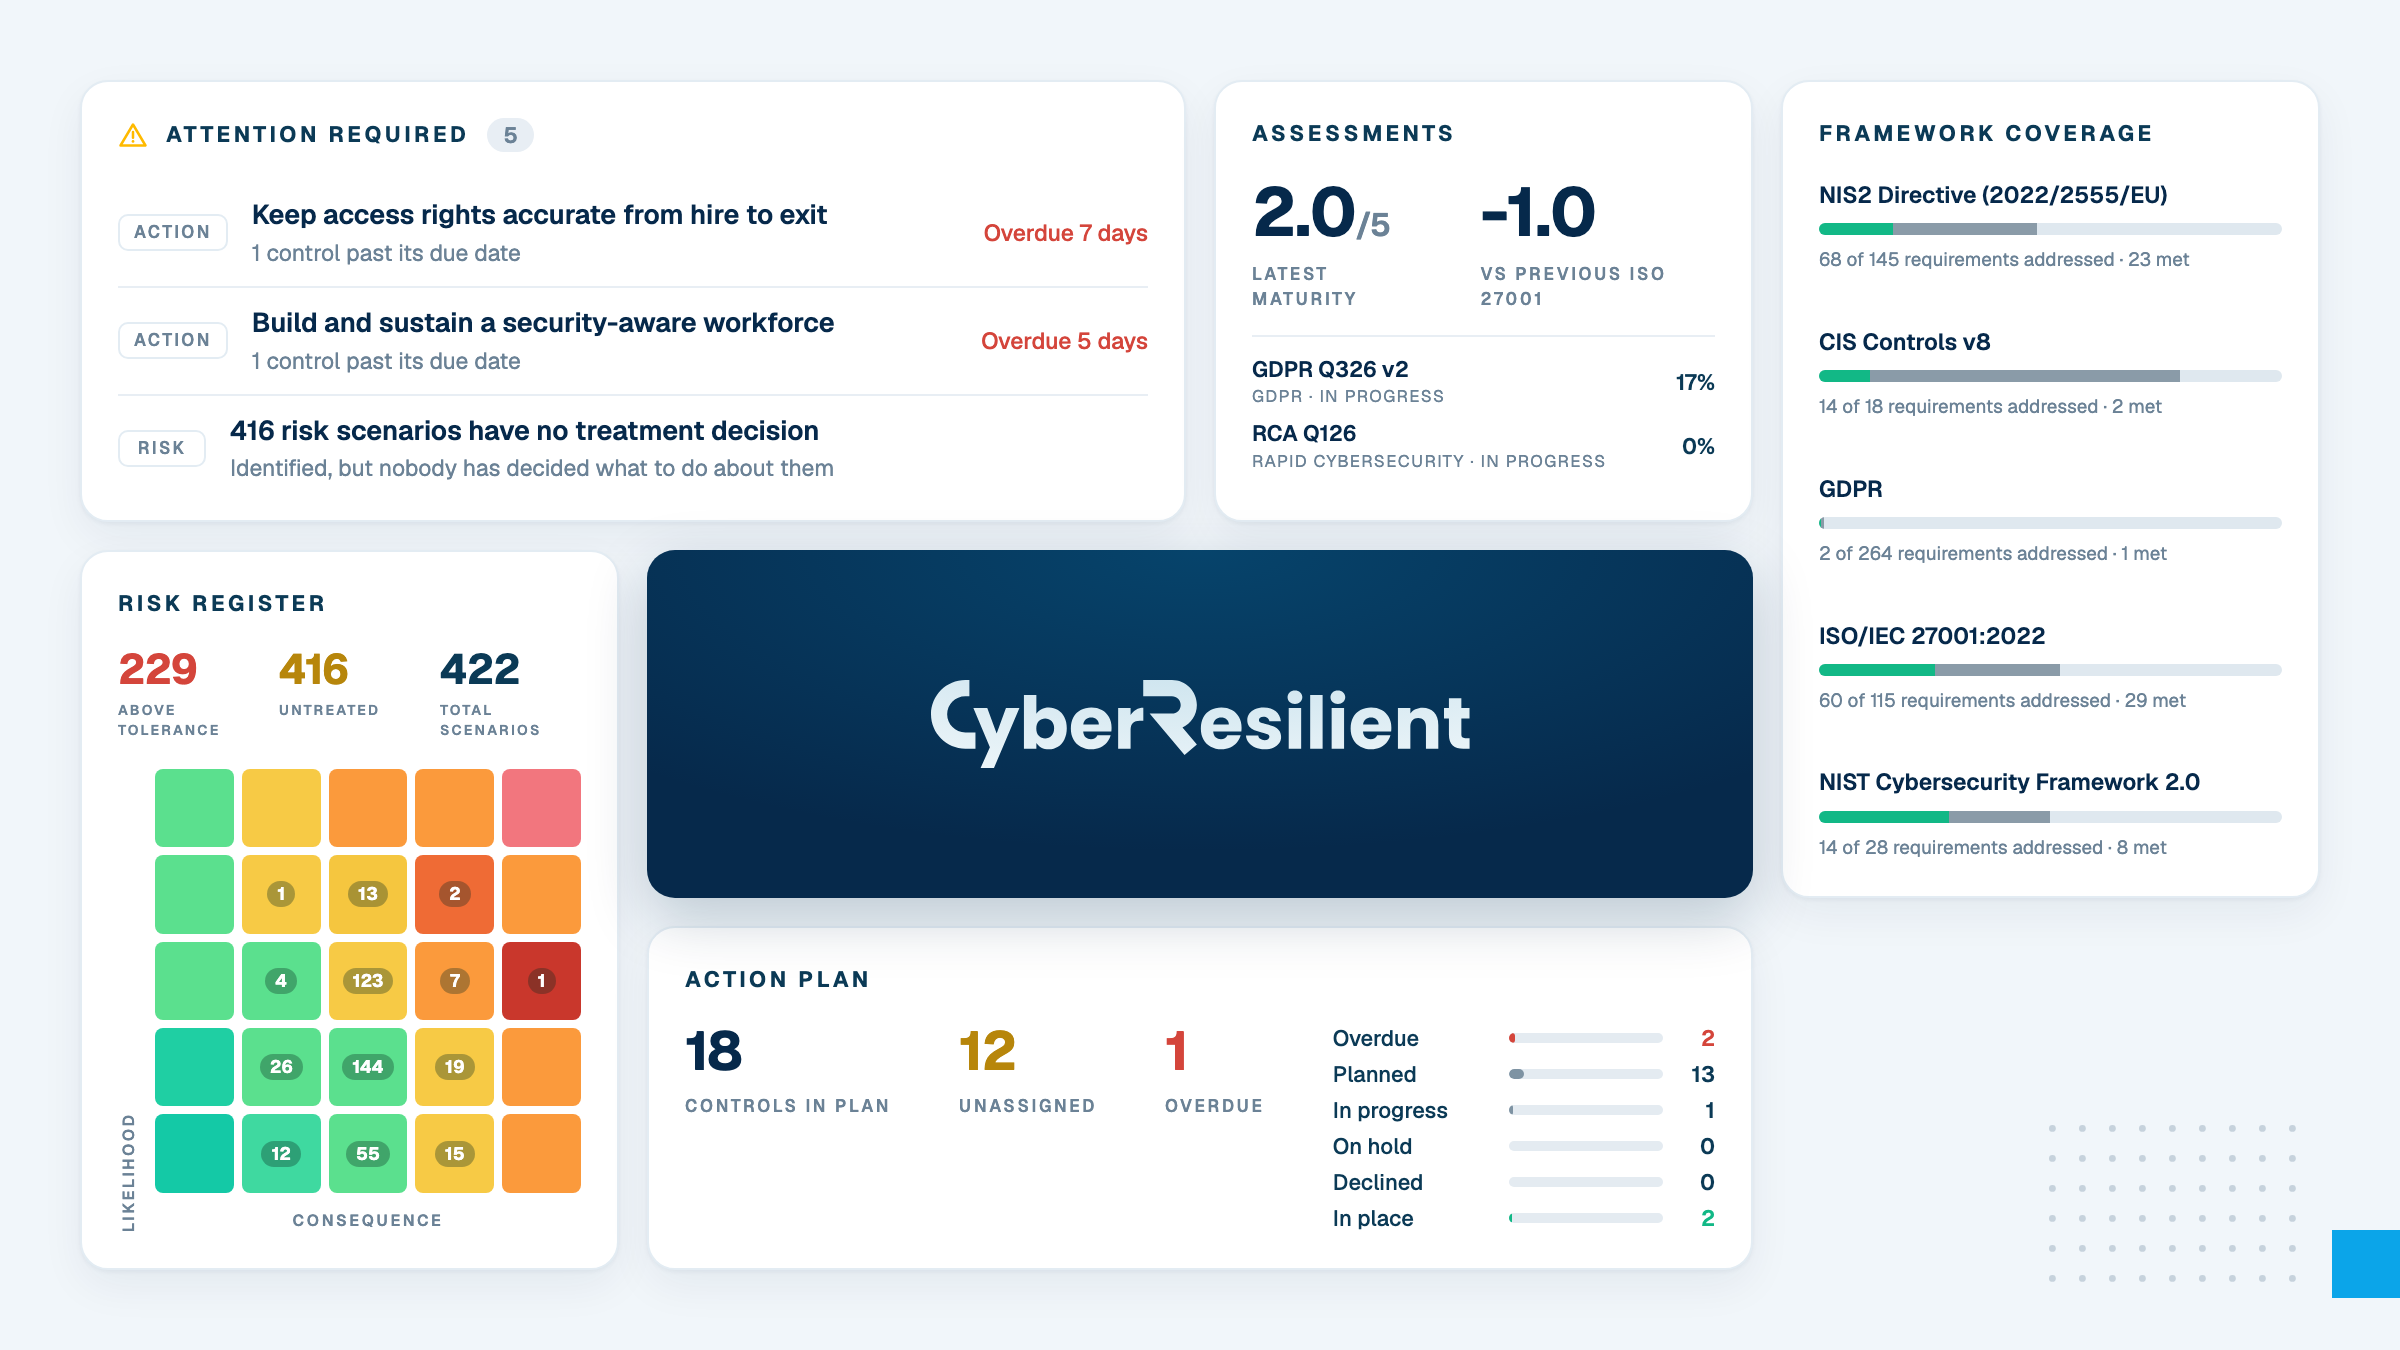
Stockholm, 22 September 2026. CyberResilient, a Swedish cybersecurity and compliance software company, has launched a new intelligent platform.
Compliance is a snapshot; resilience is a capability. Security assessments are often treated as a "false finish line," but effective risk management is the true bridge. Learn the four questions boards should be askining.
New AI tools no longer just sit alongside our work, they act within it, faster and more widely than we’ve ever seen. In this post, we will share about the new risks, the questions to ask, and agent governance.
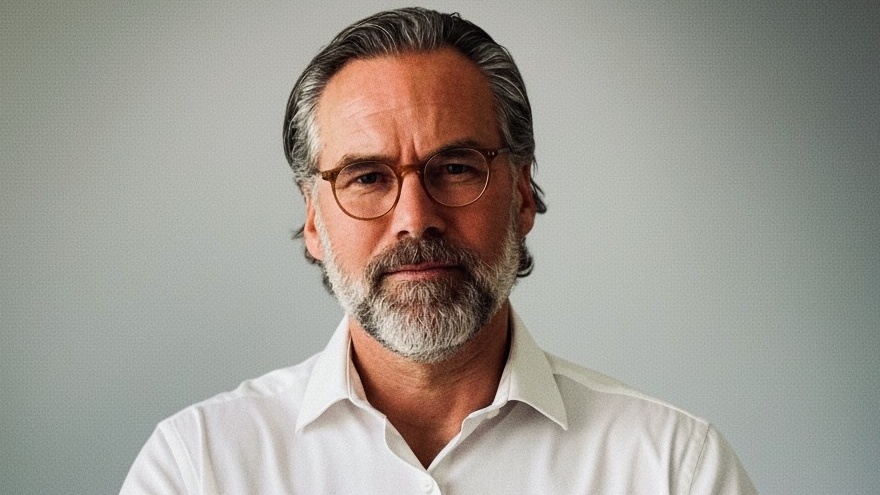
Stockholm, 2026-06-16 – CyberResilient, a Swedish software company in cybersecurity and regulatory compliance, has appointed Fredrik Limsäter as its new CEO.
Most Swedish organisations think they're further along than they are in NIS2 compliance. A gap analysis helps to demonstrate the truth. Here's what you need to know to do it correctly.
Recent cybersecurity incidents in Sweden expose different layers of the same problem: structural dependencies that have been allowed to grow without being mapped, owned, or rehearsed.